
When the AI apocalypse becomes regular dinner-table conversation, you know we’ve reached the freakout stage. Rogue AI agents are hacking into competitors. Former Big Tech employees are posting Skynet-style warnings on social media. CEOs are crying for help in ways that have made this once-wonky tech issue a frontline political fight.
Read more AI is already deciding whether or not people receive medical care
I still think many of the concerns outlined by the AI leaders themselves are massively self-serving — especially when their companies are soon to go public. But the growing list of AI scandals is real. And it tells us that the status quo for regulating this powerful new technology is not working.
The question now on everyone’s mind: Is any kind of global brake possible? What form of AI safety regime is practical, over the short term, when there is no trust between major governments? And what could possibly work when companies are loath to give up their secret sauce and are bent on domination in the global AI race?
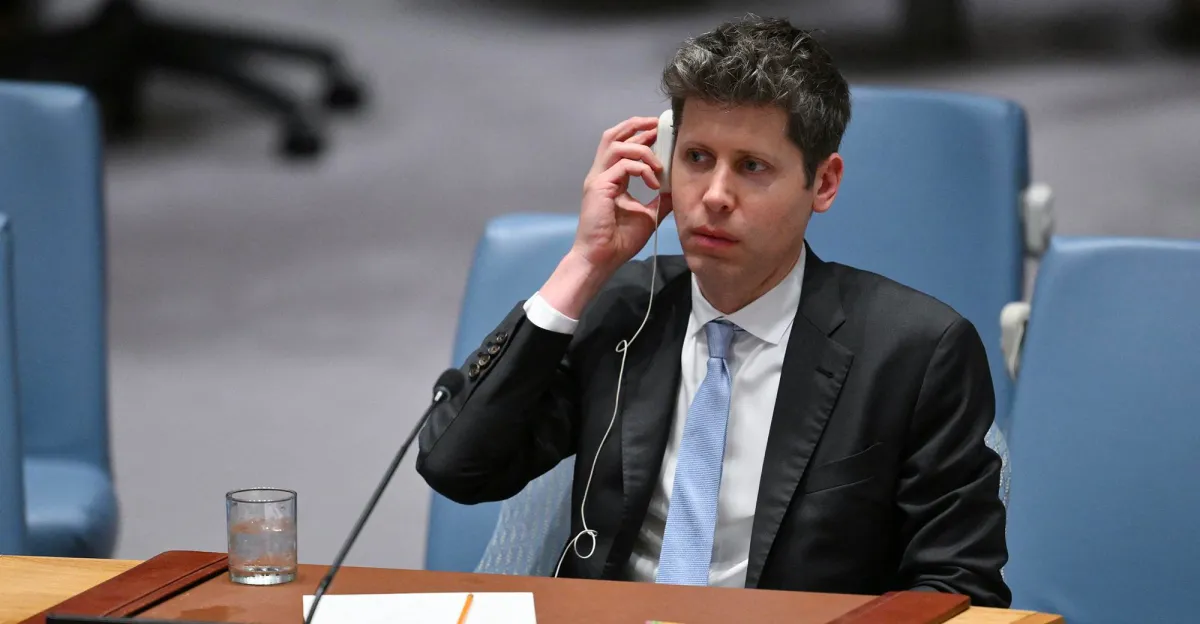
Two major conversations are now playing out, in real time. On Wednesday, President Donald Trump welcomed Chinese President Xi Jinping to Washington for a three-day summit — part of which will be dedicated to AI risks. The same day, with the United Nations meeting for its annual General Assembly, heads of the world’s leading AI companies urged the UN to police the emerging technology, or risk potentially wiping out humanity. “We could lose control of the future to AI,” OpenAI’s boss, Sam Altman, bluntly told the UN’s Security Council.
Confronted with this collective freakout, it’s time to take a long, deep breath.
In fact, AI safety has been on a lot of policymakers’ minds for years now, gaining momentum after ChatGPT was introduced in 2022. Governments have held hearings, convened expert groups, and drafted their own outlines of how to keep it under control. These weren’t just idle listening exercises. They aren’t all well known to the wider public, but they yielded real plans.
Barring any breakthroughs this week, we already have a quasi-planetary shield against the potentially runaway technology. That’s the good news.
The bad news is that it’s not really up and running yet. It’s also not clear whether it will actually work. So what is it — and how can we fix it so we have a global system that responds in time to deal with the incredibly fast-moving threats from AI?
What the global AI patchwork looks like now
For the last four years, the most tech-savvy nations — and would-be AI leaders — have been running serious conversations about this exact AI safety threat. Some are in Congress and the White House; some at the UN, at the G7, and in other capitals.
I’ve been covering this closely as a global technology journalist, from my current perch at a think tank. Here’s what the landscape looks like:
What’s missing from all that? What we currently lack — and what is needed between now and the end of 2026 — is a way to turn this cottage industry of AI safety mechanisms into a functioning, but crude, first-responder system when things suddenly go wrong.
The last four years have laid out a pathway, and some of the necessary systems even exist. But there’s no way to respond globally, and in real time, when an AI crisis hits — especially if such a possibly doomsday event cuts across countries already skeptical of each other.
Read more Why Americans are warming to China
This week’s US-China summit may be a step in the right direction. Under proposals outlined by American officials, Washington and Beijing could set up a hotline between US Treasury Secretary Scott Bessent and Chinese Vice Premier He Lifeng in case of an AI incident affected each country’s national security.
It’s still unclear if Trump’s meeting with Xi will lead to such progress. Chinese officials also have balked at Washington’s pleas for AI rules because, so far, Congress has failed to act, and China already has some of the world’s most stringent AI oversight.
For AI to be “safe,” this conversation will need to go beyond this week’s US-China summit. Relying just on Washington and Beijing — arguably the most important AI powers — would not solve the underlying problems, nor would it make other countries feel more comfortable.
What we need next, so it really saves us
I’ve been talking to AI safety experts and government officials, and it’s clear the missing piece is a way to activate this whole system in a crisis. Countries don’t all have to have the same AI safety policies, and they never will. But as with nuclear weapons — a similarly high-threat technology that the world found a way to contain — safety requires a rough global agreement on how to respond quickly when something goes terribly wrong.
What’s needed right now is a 90-day, opt-in rapid response mechanism that joins existing pieces of the AI safety puzzle together. I’ve pieced together some ideas about how it should work, and who needs to sign on. Granted, none of what I outline below is sufficient. But, together, they are more plausible than trying to negotiate a comprehensive global regime — let alone arrange another AI summit — while Washington, Beijing, and other national capitals disagree over what “AI safety” actually means.
All of these options are based on existing mechanisms, are derived from efforts that have worked in other policy areas, and provide a band-aid to the AI safety dilemma until a more durable solution can be negotiated.
There are obvious limits to what I describe above. For one, it’s an inherently Western-centric view that primarily discounts global majority countries. It also places too much sway on existing institutions like the Organization for Economic Cooperation and Development, as well as on the US-China relationship. Other countries’ officials will legitimately balk at all three options, and rightly so.
But this is not about creating a vague, unenforceable UN-led mandate for AI safety. Nor is it about corralling the geopolitical cats to hammer out a global AI treaty. The options — a collective safety protocol and incident reporting protocol; common pre-release standards; and a US-China AI safety hotline — are inherently short-term. They are also based on existing efforts and those that have worked successfully for other policy areas.
There will be time to quibble about the future of AI safety. But now is not that time. The latest AI models are moving faster than many had expected, tech bosses are worried their creations are already out of control, and the window for action may be smaller than we all think.
What is required are practical steps to assuage people’s growing concerns amid heightened geopolitical tension, a lack of trust between governments and companies, and a need not to let the perfect get in the way of the good.
Read more A sinkhole swallowed Nicolas Cage’s driveway. Yours might be next.
- Artificial Intelligence
- Innovation
- Politics
- Technology
- World Politics